CVE-2026-98432 is a use-after-free in the Linux kernel’s IPv4 TCP connection setup, present since 4.4 and scored 9.8 by the kernel CNA. Anthropic says its AI model built a no-credentials root exploit against a host with a multipath TCP listener. Debian, Oracle and Amazon Linux have fixed kernels; Ubuntu and RHEL do not. This post covers the mechanism, who is exposed, when to rush, how Fleet finds the hosts, an interim mitigation script, and two policies that apply it on check-in and remove it once the patched kernel is running.
CVE-2026-111497 is a buffer overflow in Google’s Brotli decoder (1.0.3 to 1.2.0) that is compiled into Node.js, Bun, Envoy, Python Brotli wheels, .NET and the browsers. A crafted Content-Encoding: br body reaches it with no login. The upstream fix is tiny; finding every bundled copy is the work. This post ships six Fleet queries with version logic that does not trust SQLite string comparison, a policy pattern, and what the queries found on a real fleet (hint: Pillow bundles libbrotli 1.2.0).
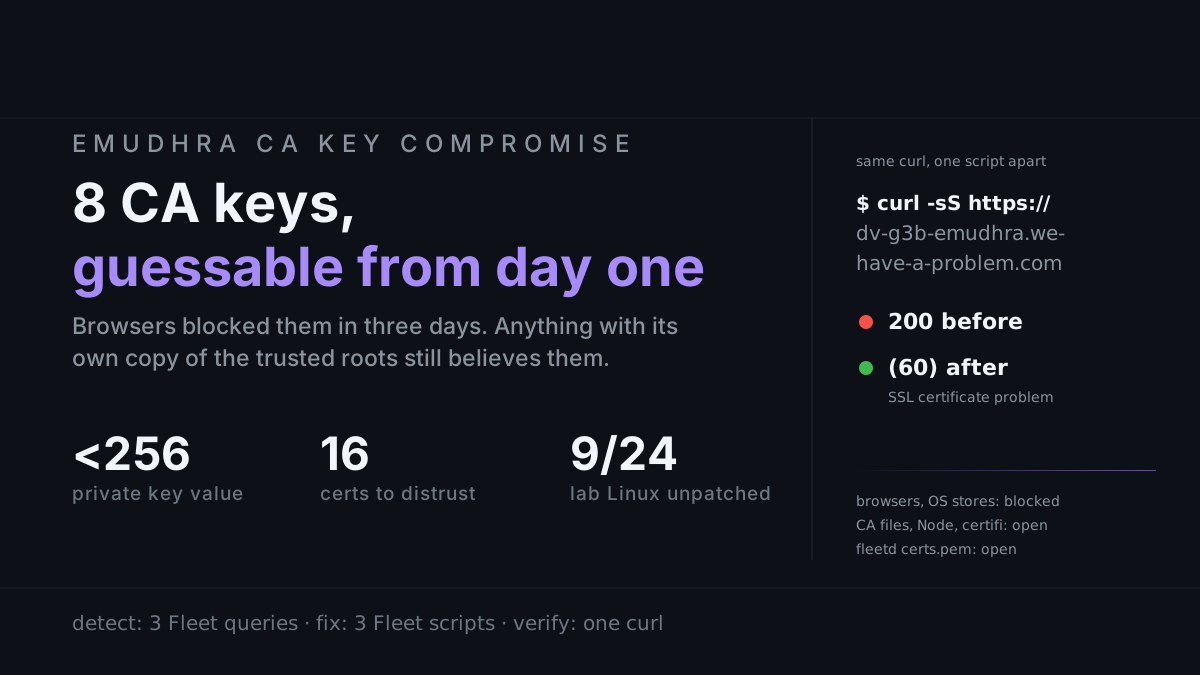
Eight eMudhra intermediate CA keys were generated as tiny, guessable numbers, so anyone can forge a trusted certificate for any website. Browsers and operating systems blocked them within three days. Everything that keeps its own copy of the trusted roots did not: Linux CA bundles, macOS /etc/ssl/cert.pem, Node.js, Python certifi, and the CA bundle Fleet’s own agent uses to reach the Fleet server. This brief explains the blast radius in plain words and ships three Fleet queries and three Fleet scripts (macOS, Windows, Linux) that find and fix the exposure, tested on real hosts and containers.
Your EDR knows about processes and network connections. Your MDM knows about installed apps. Neither one knows that someone on your team is running an npx-fetched MCP server that has shell-exec capability and a plaintext secret baked into its config. agentic-detector is a cross-platform osquery extension that fixes that. One table — ai_tools — gives you the full AI software inventory per host: MCP servers, agent CLIs, IDE plugins, desktop apps, live network sockets, and the agent instruction files that tell AI what it’s allowed to do. Deployable through Fleet in minutes.
GHSA-p58x-r3c9-x9p6 is a path-traversal bypass of the CVE-2026-48800 patch in Notepad++ v8.9.6.1, fixed in v8.9.6.2. It carries no CVE of its own, so vulnerability scanners that key on CVE catalogs may not flag it — and even when they do, they catch the registry-installed program while a portable notepad++.exe dropped in Downloads goes unseen. This post validates the advisory, then ships a Fleet/osquery identification query and a policy that fails when a vulnerable copy is present, installed or portable.
ClickFix is the most active cross-platform initial-access technique of 2026 — fake CAPTCHAs and support prompts that silently copy a malicious command to the clipboard, instruct the user to paste it into the Windows Run dialog or macOS Terminal, and deliver infostealers (Lumma, AMOS), remote-access tools (NetSupport RAT), and AppleScript keychain stealers. No code-execution vulnerability is exploited — the victim is the delivery mechanism. This brief walks the five-stage attack flow, lists atomic indicators, and ships a Fleet/osquery detection pack with every query validated against the current Fleet table schema.
Trend Micro disclosed SHADOW-EARTH-053 on 30 April 2026 — a China-aligned cyberespionage campaign exploiting ProxyLogon against unpatched Microsoft Exchange and IIS to deploy GODZILLA web shells and ShadowPad across South, East, and Southeast Asia plus one NATO target. This brief documents the campaign through Lockheed’s seven kill-chain stages with a Diamond Model rendered for each stage, consolidates the atomic indicators, and ships a vetted Fleet/osquery detection pack. Every query in the pack has been audited against fleetdm.com/tables before publication — schema bugs in the publicly circulating versions are called out and corrected inline.